
Cybersecurity area
Network Security
Network Security protects communication between users, applications, data centers, branches, cloud services, partners, and the internet.

Acronym Glossary
This glossary explains acronyms used in this part so the intended security function is clear.
- NGFW
- Next-Generation FirewallA firewall combining application control, IPS, VPN, user context, and security functions.
- IDS
- Intrusion Detection SystemA system for detecting suspicious or malicious network activity without directly blocking traffic.
- IPS
- Intrusion Prevention SystemA system for detecting and actively blocking malicious network activity inline.
- NDR
- Network Detection and ResponseDetection and response based on network traffic, metadata, and communication anomalies.
- VPN
- Virtual Private NetworkAn encrypted network tunnel for remote access or network interconnection.
- ZTNA
- Zero Trust Network AccessAn access model that verifies identity, context, and authorization before access to a specific application.
- DDoS
- Distributed Denial of ServiceA distributed availability attack that floods a service with traffic or requests.
- CDR
- Content Disarm and ReconstructionA technology that removes active or risky content from files and creates a safer version of the document.
What This Area Covers
Network Security protects communication between users, applications, branches, data centers, cloud, partners, and the internet. The network is no longer a simple perimeter. It is a set of connections between local infrastructure, SaaS services, remote users, API interfaces, OT environments, and external partners.
Why It Matters
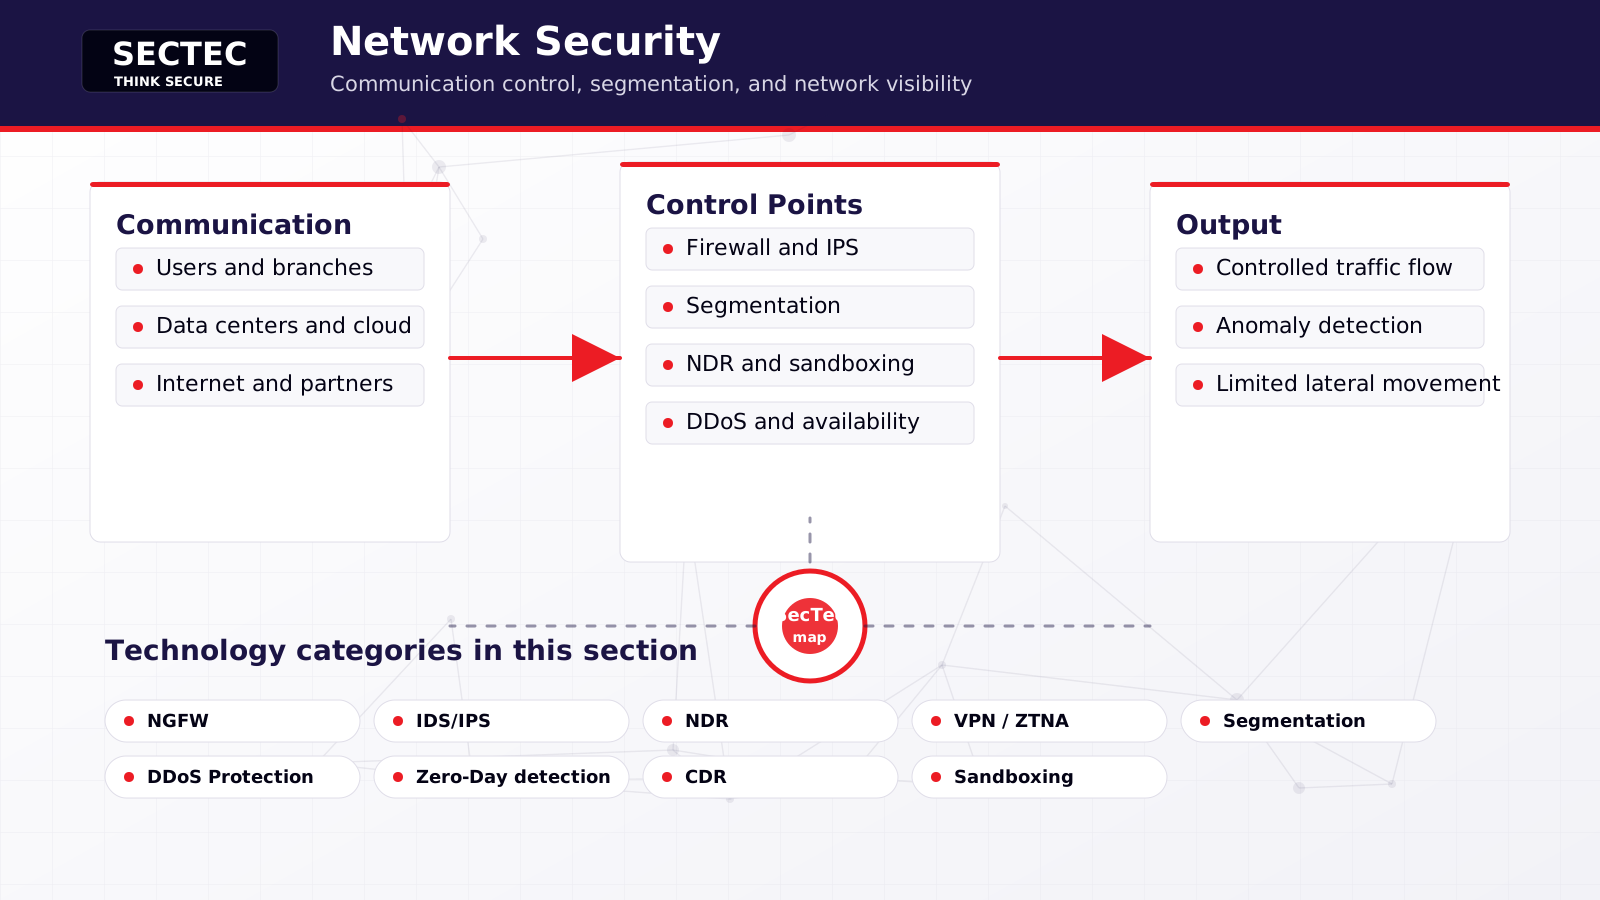
The value of network security lies in controlling communication flows and understanding what is happening in the network. Firewalls, IDS/IPS, NDR, VPN/ZTNA, segmentation, DDoS protection, sandboxing, and zero-day detection address different types of risk. Some technologies block traffic inline, while others monitor behavior passively and provide context to security teams.
How To Navigate This Area
Network security combines access control, segmentation, monitoring, anomaly detection, and availability protection. It is important to determine whether a technology should enforce rules inline, work passively over traffic telemetry, or act as an analytical layer for security teams. Hybrid environments also require ZTNA, cloud connectivity, lateral movement detection, and DDoS resilience.
The core question is whether the organization needs to enforce rules, gain visibility, protect availability, or limit attacker movement inside the network. NGFW and segmentation control communication, NDR detects anomalies and lateral movement, DDoS protects service availability, and VPN/ZTNA provides secure access for users and partners.
The technology list below works as a map of the Network Security area. The practical sequence is to name the security problem first, select the closest technology category second, and only then compare relevant vendors. This helps separate similar-sounding solutions and reduces the risk of adding another tool without a clear architectural role.
Technical Section Schema
Questions To Ask When Selecting A Solution
- Where are the most important control points: perimeter, branches, cloud, data center, or remote access?
- Should the technology block traffic, analyze it, or mainly add visibility?
- Is DDoS availability protection needed, or rather segmentation and lateral movement detection?
- How will network events connect to SIEM, SOAR, XDR, NDR, or cloud telemetry?
How To Use This Section
Each technology page expands one category, explains its architectural role, and lists SecTec portfolio vendors related to that area. The section page is therefore the orientation layer, while the detail pages support concrete mapping to solutions.
Vendors From The SecTec Portfolio
Attack coverage and defensive context
MITRE ATT&CK® Enterprise version 19.1 is used as a reference model. The mapping is a SecTec expert interpretation and does not imply endorsement by MITRE.
Practical attack scenarios
- Phishing and identity abuseAn adversary manipulates a user, obtains credentials, or abuses a trusted account to gain access to the environment.
- Credential theftAn adversary obtains passwords, tokens, sessions, or other authentication material and uses it to expand access.
- Public application or API abuseAn adversary exploits a vulnerable web application, API, client-side code, or software component for initial access and execution.
- Cloud and SaaS compromiseAn adversary abuses cloud identities, permissions, configurations, or application integrations to access services and data.
- Lateral movement inside the networkAfter initial access, an adversary discovers systems, accounts, and services and moves toward higher-value assets.
- Malware and Command and ControlMalicious code executes, maintains access, and communicates with adversary infrastructure through common or covert channels.
- Ransomware and availability impactAn adversary encrypts or manipulates data, stops services, inhibits recovery, and creates operational impact.
- Supply chain and trusted accessAn adversary abuses a supplier, software dependency, external access path, or trusted relationship to bypass normal controls.
- Attacks on OT and IoT environmentsAn adversary discovers industrial or connected devices, abuses remote access and network services, and threatens operational availability.
- Reconnaissance and attack surface mappingAn adversary collects information about people, systems, cloud services, and internet-facing infrastructure and searches for a viable initial-access path.
- Business Email Compromise and mailbox takeoverAn adversary takes over or impersonates a trusted email identity and abuses communications for fraud, payment diversion, data collection, or further phishing.
- Privilege escalation and persistenceAn adversary expands privileges, creates or modifies accounts and policies, and establishes repeatable access to systems, identities, or cloud environments.
- Defense evasion and control impairmentAn adversary hides activity, removes evidence, disguises code, or weakens security tools, encryption, firewalls, and recovery mechanisms.
- Insider threat and authorized access abuseAn insider or an adversary with a valid account abuses legitimate permissions to discover, copy, manipulate, or transfer sensitive data.
- DDoS and resource exhaustionAn adversary floods a network, application, API, or endpoint and exhausts capacity, connections, or compute resources to reduce service availability.
- API resource and cost exhaustionAn adversary abuses expensive API operations, large inputs, or paid services to exhaust CPU, memory, storage, connectivity, or financial limits.
- Sensitive business flow and bot abuseAn automated adversary abuses legitimate functionality such as purchasing, booking, registration, voting, commenting, or account recovery.
- SSRF – Server-Side Request ForgeryAn adversary causes a server or API to fetch an attacker-controlled address and reaches internal services, cloud metadata, or protected network targets.
- Shadow and zombie APIs without managed inventoryUnknown, forgotten, or outdated API versions remain reachable without current controls, ownership, documentation, and monitoring.
- Credential stuffing and password sprayingAn adversary automatically tests leaked username-password pairs or a small set of common passwords against many accounts.
- Injection and command executionUntrusted input changes the meaning of a command, query, or template and enables data access, logic bypass, or code execution.
- Malicious file upload and unsafe deserializationAn application accepts or processes a malicious file or serialized object and enables code execution, control bypass, or compromise of other users.
Relevant ATT&CK techniques
- T1018 · Remote System DiscoveryDetect, Respond
- T1021 · Remote ServicesDetect, Prevent, Respond
- T1027 · Obfuscated Files or InformationDetect, Prevent, Validate
- T1040 · Network SniffingDetect, Respond
- T1046 · Network Service DiscoveryDetect, Prevent, Respond
- T1059 · Command and Scripting InterpreterDetect, Prevent, Validate
- T1071 · Application Layer ProtocolDetect, Prevent, Respond
- T1078 · Valid AccountsDetect, Prevent
- T1090 · ProxyDetect, Respond
- T1095 · Non-Application Layer ProtocolDetect, Prevent, Respond
- T1105 · Ingress Tool TransferDetect, Prevent, Respond, Validate
- T1133 · External Remote ServicesDetect, Prevent
- T1189 · Drive-by CompromiseDetect, Prevent, Validate
- T1190 · Exploit Public-Facing ApplicationDetect, Prevent, Respond, Validate
- T1204 · User ExecutionDetect, Prevent, Validate
- T1210 · Exploitation of Remote ServicesDetect, Prevent, Respond
- T1498 · Network Denial of ServiceDetect, Prevent, Respond
- T1499 · Endpoint Denial of ServiceDetect, Prevent, Respond
- T1550 · Use Alternate Authentication MaterialDetect, Prevent
- T1557 · Adversary-in-the-MiddleDetect, Respond
- T1573 · Encrypted ChannelDetect, Respond
- T1686 · Disable or Modify System FirewallDetect, Prevent, Respond